Mirae Asset Finance Alleges Rs 8.92 Crore Loan Disbursement Fraud via API in Four Hours, Navi Mumbai Cyber Police Register Case
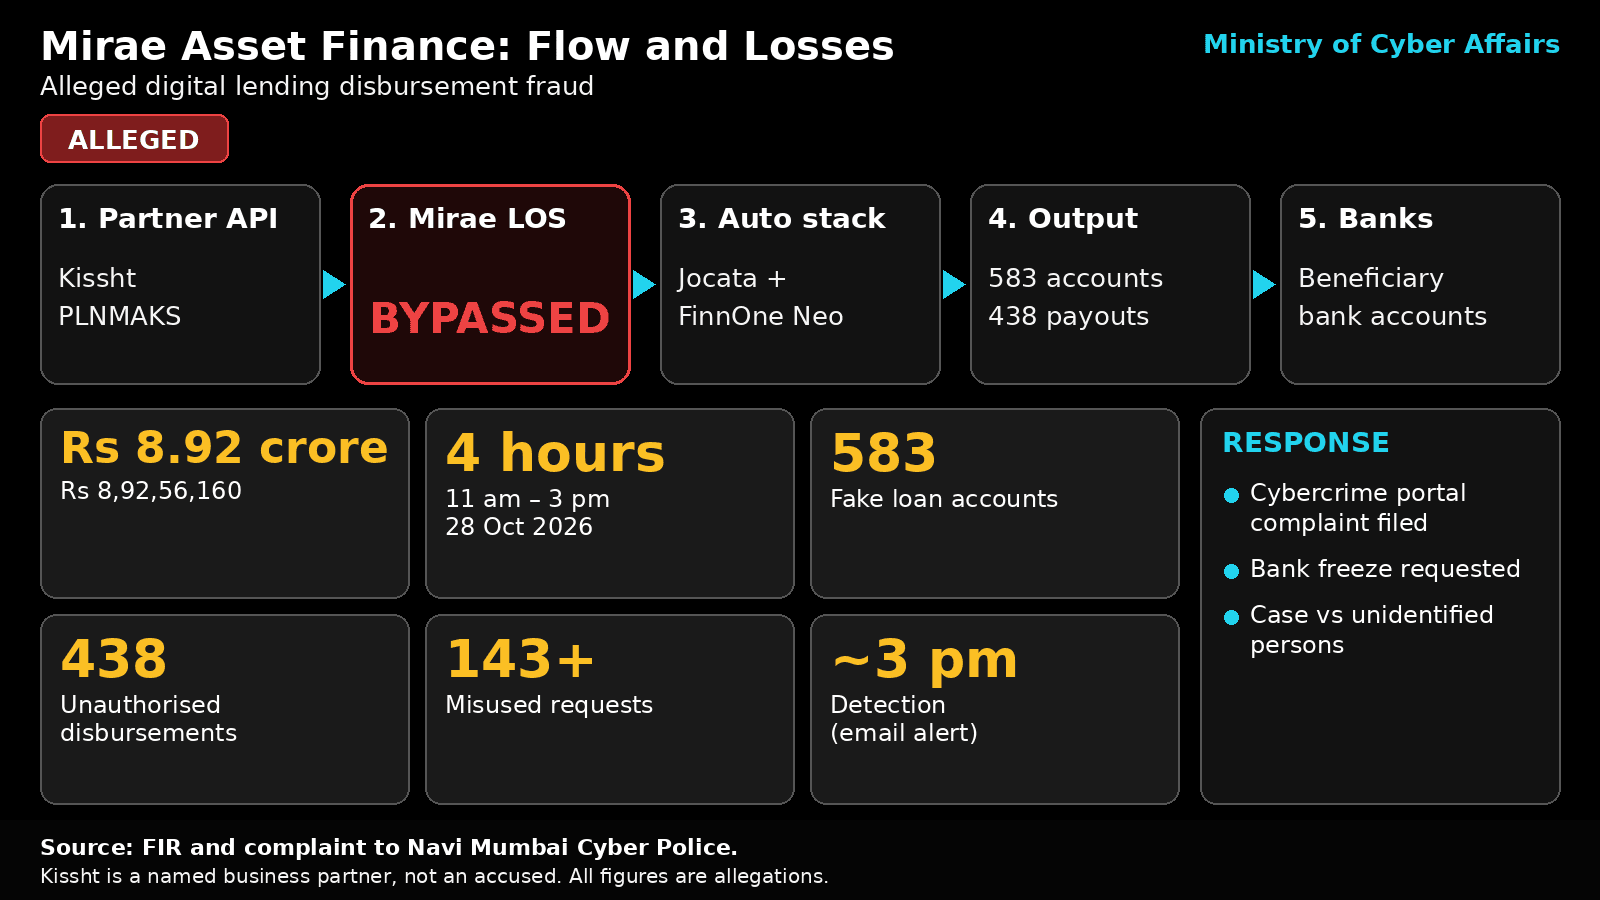
Navi Mumbai Cyber Police registered a case after Mirae Asset Financial Services (India) alleged Rs 8,92,56,160 was siphoned in four hours on 28 Oct 2026 via 583 fictitious loans and 438 disbursements, with product code PLNMAKS linked to partner Kissht. FIR number not published.
Navi Mumbai Cyber Police have registered a case against unidentified persons after Mirae Asset Financial Services (India) Private Limited alleged that cyber fraudsters siphoned Rs 8,92,56,160 (Rs 8.92 crore) from its automated digital-lending stack in about four hours on 28 October 2026.
What the complaint alleges
According to the complaint, unauthorised activity ran from about 11 am to 3 pm.
Investigators suspect the accused bypassed the company’s Loan Origination System and used product code PLNMAKS, associated with business partner Kissht, to generate 583 fictitious loan accounts.
More than 143 misused requests allegedly drove 438 unauthorised disbursements into multiple bank accounts.
Detection came around 3 pm after an email alert about a failed disbursement.
The company complained on the National Cyber Crime Reporting Portal and contacted its bank to freeze funds.
According to local reports, around Rs 40 lakh was later secured in some beneficiary accounts.
Police coverage names IT Act sections 43, 66C and 66D plus relevant Bharatiya Nyaya Sanhita provisions. The news was first reported by Newslaundry.
Companies and products involved
- Mirae Asset Financial Services (India) Pvt Ltd is an RBI-registered non-deposit-taking Investment and Credit Company (CoR N-13.02408; CIN U65999MH2020PTC337638), part of the Mirae Asset financial group’s India lending arm, with operations including Airoli, Navi Mumbai.
- Kissht is a digital consumer-credit brand operated by OnEMI Technology Solutions Limited; lending on the Kissht/Ring channel is associated with regulated partners including NBFC subsidiary Si Creva Capital Services.
In this case, Kissht appears only as a named business partner and product-code path. Coverage does not accuse Kissht of wrongdoing.
- Jocata (digital-lending / credit-decision stack) and FinnOne Neo (Nucleus Software’s digital lending / loan origination platform) are described in the complaint as systems used for automated verification and disbursement (~2 minutes).
They are not named as accused parties, and this article does not claim a product defect.
Related context, not proof of the same actors
On 9 October 2026, CERT-In / CSIRT-Fin advisory CIAD-2026-0046 warned NBFCs and fintechs about stolen payment/disbursement API credentials used to invoke payout APIs from whitelisted infrastructure.
A separate Delhi Police NBFC unauthorised-transfer case earlier in October shows a similar sector pattern, not proof of the same actors here.
What other lenders should check
Without inventing case-specific root causes, RBI digital-lending expectations and CERT-In’s advisory point lenders toward hardening partner APIs and payout paths:
- inventory and disable unused endpoints;
- replace long-lived static tokens;
- enforce MFA on admin and banking APIs;
- bind loan stages cryptographically;
- maker-checker for disbursements;
- validate every payout against sanctioned loan records and beneficiary checks;
- set API-level amount and velocity limits;
- monitor failed/high-rate disbursement alerts in real time;
- and preserve logs for forensic handoff to cyber police.
All details are allegations under investigation; the FIR number and investigating officers have not been published.