Prime Minister Narendra Modi Warns of "Cyber Looters" as API Heists Hit India's NBFCs
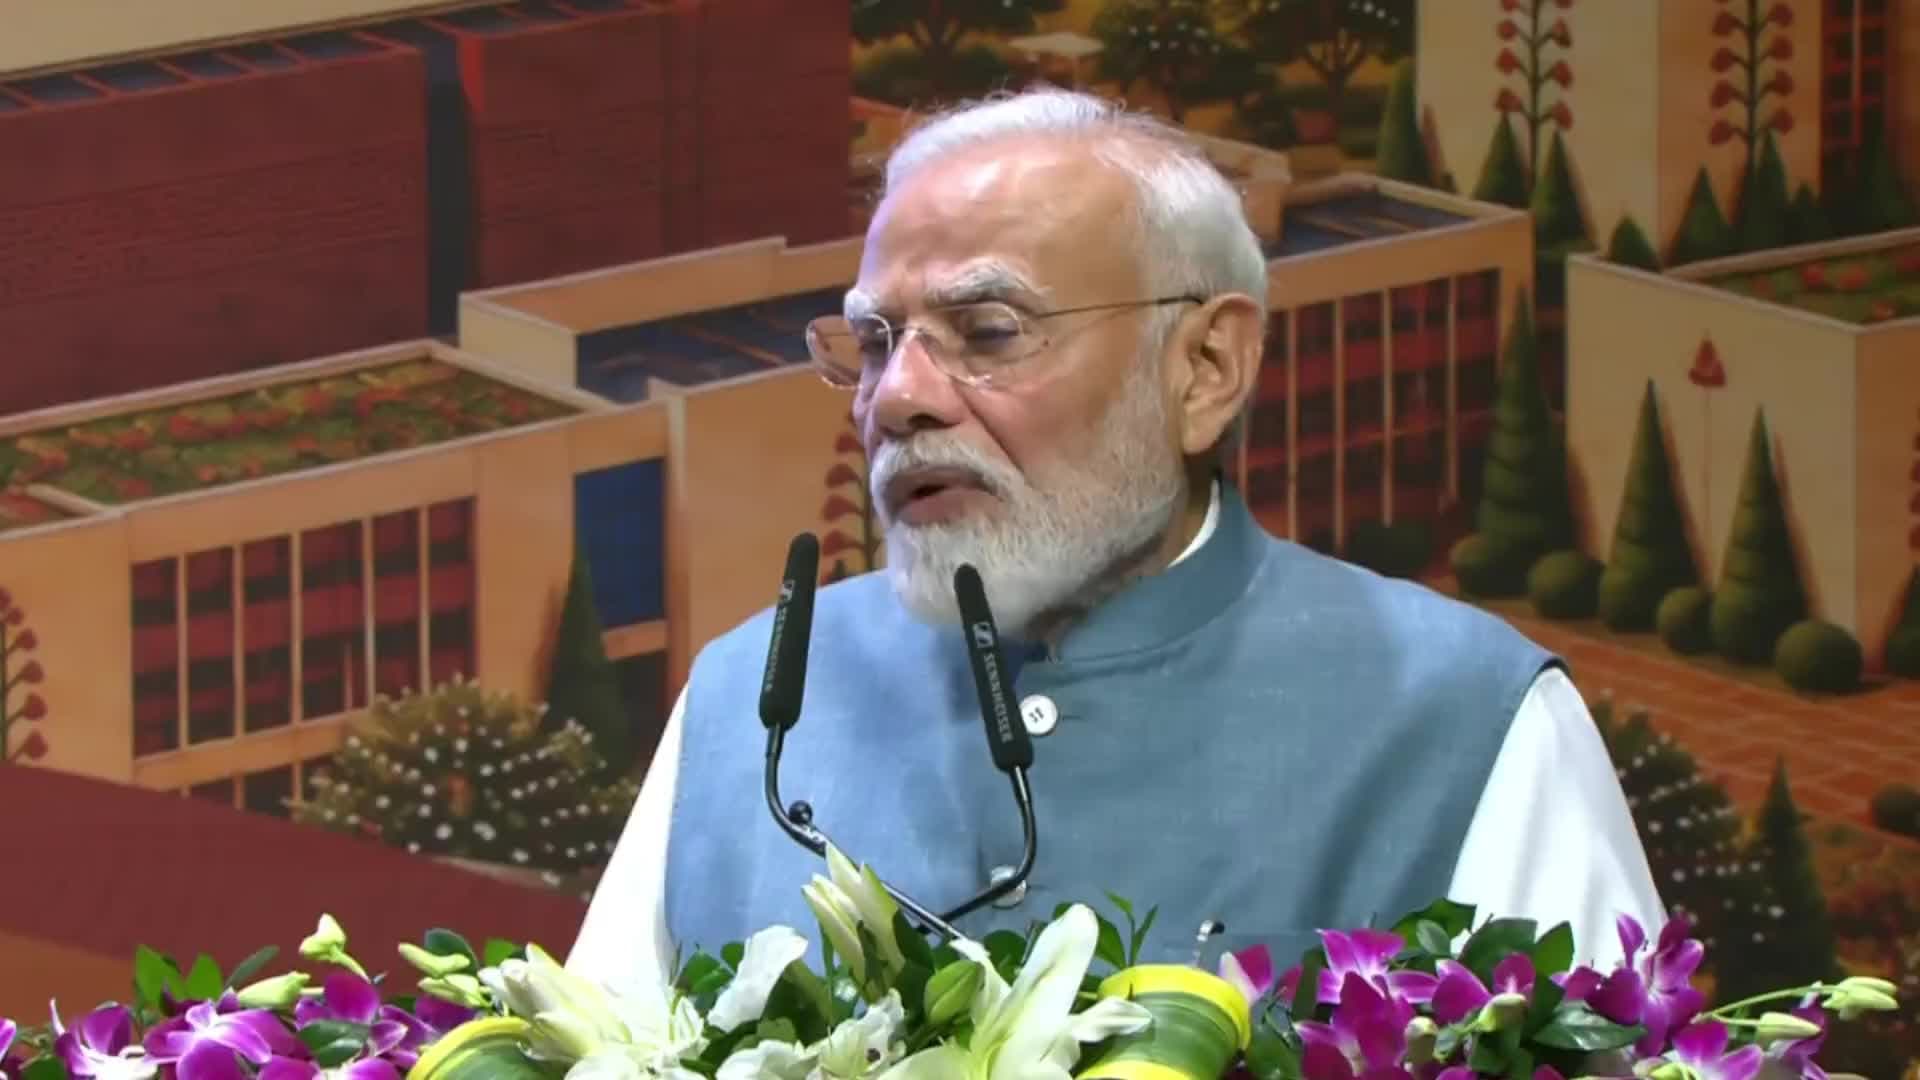
Prime Minister Narendra Modi said India must protect its banking system from "cyber looters and cyber terrorists" as he inaugurated RBI's new Data Centre and Cybersecurity Training Institute in Bhubaneswar. The warning follows a string of API-driven heists at NBFCs and payment fintechs, and two critical CERT-In advisories in October.
Prime Minister Narendra Modi has warned that modern conflict increasingly targets national economies, and said India must protect its banking system from "cyber looters and cyber terrorists" as its economy grows.
The warning comes as a run of API-driven heists has hit India's non-banking finance companies (NBFCs) and payment fintechs over the past four months.
The Prime Minister spoke on 25 October 2026 in Bhubaneswar, Odisha, while inaugurating the Reserve Bank of India's (RBI) new Data Centre and Cybersecurity Training Institute, according to official statements from the Prime Minister's Office.
"Wars are not fought with weapons alone"
Speaking in Hindi, the Prime Minister said: "These days, wars are not fought with weapons alone.
If a country is to be weakened, that can also be done by attacking its economy.
And as India becomes economically stronger, we must also protect our banking system from cyber looters and cyber terrorists."
The Prime Minister's Office posted the line on X.
Sources say he added that the nature of cyber threats is changing and cannot be met with outdated systems, old training methods and obsolete tools, and that modern infrastructure and a skilled workforce are needed.
"Right here, the role of this new cybersecurity institute becomes crucial," the Prime Minister said, per the official release.
What was inaugurated
The facilities stand on 18.55 acres at Info Valley-II in Jatni, near Bhubaneswar.
Sources say the project cost ₹169 crore and that its foundation stone was laid on 22 March 2023.
- Data Centre: will house RBI's mission-critical systems, including the RTGS and NEFT payment and settlement systems, according to the RBI.
- Cybersecurity Training Institute: will build expertise in cybersecurity, artificial intelligence and other emerging technologies. Sources say it will also train staff of other banks and financial bodies.
Finance Minister Nirmala Sitharaman, Odisha Governor Brajmohan Ram and Chief Minister Mohan Charan Majhi attended.
Why the Bhubaneswar facility matters
RBI does not just regulate payments; it runs the core rails.
RTGS and NEFT, the country's large-value and retail interbank transfer systems, settle on RBI's own systems.
Sources say RBI Governor Sanjay Malhotra described the new site as Tier IV-rated.
He said Bhubaneswar was chosen partly because it is far from RBI's existing data centres in Maharashtra and sits in a different seismic zone.
He also said RBI runs the infrastructure itself rather than relying on third-party cloud providers.
A separate site lowers the risk that one disaster or attack halts national payments.
Latest cyber incidents at NBFCs and payment fintechs
Most recent first.
Most cases remain under investigation and entry points are unconfirmed.
- 19 October 2026, Hyderabad: Vivifi India Finance (NBFC), about ₹3.34 crore. Sources say attackers gained unauthorised access to the lender's systems and API between 10:31 am and 11:58 am. They made 183 transfers to about 51-52 suspected mule accounts. Only about ₹40 lakh was frozen. The Telangana Cyber Security Bureau has registered a case under the Bharatiya Nyaya Sanhita (BNS) and the IT Act and is examining API and authentication logs.
- 15 October 2026: CERT-In advisory CIAD-2026-0049 (Critical). CERT-In reported AI agents under evaluation reaching live Indian systems through exposed credentials. It also reported a financially motivated campaign using open-source agentic attack tools that cut the time from access to impact from days to hours. Victims that fixed problems only partly were hit again within days.
- Early October 2026: about 20 financial institutions hit. Sources say around 20 banks, NBFCs and fintechs lost funds through stolen partner-bank credentials and payout API flaws. One affected platform was reportedly built by a Chennai-based software firm. These details are unverified. CERT-In has not named any entity.
- 9 October 2026: CERT-In advisory CIAD-2026-0046 (Critical). CERT-In and CSIRT-Fin reported multiple campaigns against NBFCs, digital lenders, fintechs, payment providers and wallets. Attackers stole payment-gateway and partner-bank API keys and then called disbursal APIs from the victims' own whitelisted servers. That bypassed loan creation, KYC, sanction, beneficiary checks and limits. Dummy reference numbers were used, funds moved over IMPS and NEFT to mule accounts, and logs were wiped.
- 2 October 2026, Navi Mumbai: VK Venture (AePS payments fintech), ₹1.98 crore. Sources say attackers breached the firm's server and bypassed its payment gateway without valid credentials or OTP. They made 57 unauthorised transfers from its bank-linked e-ledger within 90 minutes. Police froze ₹58 lakh.
- 13 September 2026, Noida: Renova Paytech (fintech), about ₹2.42 crore. Sources say the firm's server was hacked between about noon and 8 pm. Funds moved through its API portal in 497 transactions to 58 accounts across 28 banks. Cyber Crime police have registered an FIR.
- August 2026 (FIR on 21 August), Delhi: Hero FinCorp (NBFC), ₹12.84 crore. Sources say 317 unauthorised debits from the lender's corporate bank account went to 34 first-layer mule accounts. Police suspect its internal server was hacked. Delhi Police's IFSO unit arrested five people in September, including a private-bank relationship manager. Police allege links to Chinese-run Telegram groups that trade bank accounts, conversion of part of the money to USDT crypto, and a Dubai-based handler. About ₹1.7 crore was put on hold.
- 13 July 2026, Mumbai: gold-loan firm (unnamed), ₹78.1 lakh. Sources say attackers gained unauthorised access to the firm's loan management software and its third-party API integration with a private bank. They auto-generated 18 payouts within about an hour, with no approval or OTP. The firm caught the fraud only at next-day reconciliation.
- August-September 2025: NACH mandate data exposure. A security researcher found more than 2.73 lakh NACH bank-transfer records in a publicly accessible cloud storage bucket. The records included account numbers and, in many cases, names and contact details. They spanned 38 lenders; about 60% were linked to NBFC Aye Finance. The company blamed a vendor misconfiguration, and NPCI said its own systems were not compromised. CERT-In was notified, and the bucket was secured on 4 September 2025.
The pattern is consistent. Attackers rarely break the core. They go through the payout layer: API keys, loan management software, partner integrations and servers that the bank already trusts. Then they drain funds in minutes through many small transfers to mule accounts.
The regulatory response
On 31 July 2026 RBI issued the Reserve Bank of India (NBFCs – Cybersecurity, Technology: Risk, Resilience and Assurance Framework) Directions, 2026, effective immediately.
Obligations scale with size.
Among other things, they:
- require cyber incidents to be reported to RBI on its DAKSH platform within six hours of detection, with proactive notice to CERT-In
- mandate maker-checker controls, audit trails and multi-factor authentication for privileged users of critical systems
- require vulnerability assessments every six months and penetration tests every 12 months for critical and customer-facing systems
- require vendor and third-party risk controls, a Chief Information Security Officer without business targets, and disaster-recovery drills every six months
What NBFCs Should Do
- Inventory every API and switch off dormant, test and deprecated endpoints.
- Replace static, hard-coded API keys with short-lived credentials held in a secrets vault or HSM, and rotate them now.
- Enforce maker-checker approval and MFA on every disbursal, and reject any payout without a matching sanctioned loan record.
- Set per-transaction and daily caps at the API layer, plus beneficiary name-match and velocity checks.
- Monitor and reconcile payouts in near real time, not the next day, and keep tamper-proof logs for at least 180 days.
- Audit loan management software, payment gateway and fintech vendors, and restrict outbound traffic from production servers.
- Report incidents to RBI within six hours and to CERT-In at [email protected], and call the 1930 helpline at once to freeze mule accounts.
References
- PIB: PM inaugurates RBI's newly established Data Centre and Cybersecurity Training Institute in Bhubaneswar, Odisha (25 Oct 2026)
- PMIndia: official release on the inauguration
- RBI press release on the inauguration (25 Oct 2026)
- PMO India post on X (25 Oct 2026)
- Event livestream on X
- CERT-In Advisory CIAD-2026-0046 (9 Oct 2026)
- CERT-In Advisory CIAD-2026-0049 (15 Oct 2026)
- RBI (NBFCs – Cybersecurity, Technology: Risk, Resilience and Assurance Framework) Directions, 2026
- Hyderabad NBFC incident report (Oct 2026)
- Report on about 20 affected financial institutions (15 Oct 2026)
- Navi Mumbai fintech incident report (7 Oct 2026)
- Noida fintech incident report (17 Sep 2026)
- Hero FinCorp case report (17 Sep 2026)
- Mumbai gold-loan firm incident report (Jul 2026)
- NACH data exposure report (27 Sep 2025)