How a "Laptop Farm" Works - advisory issued by Japan against North Korean group WaterPlum
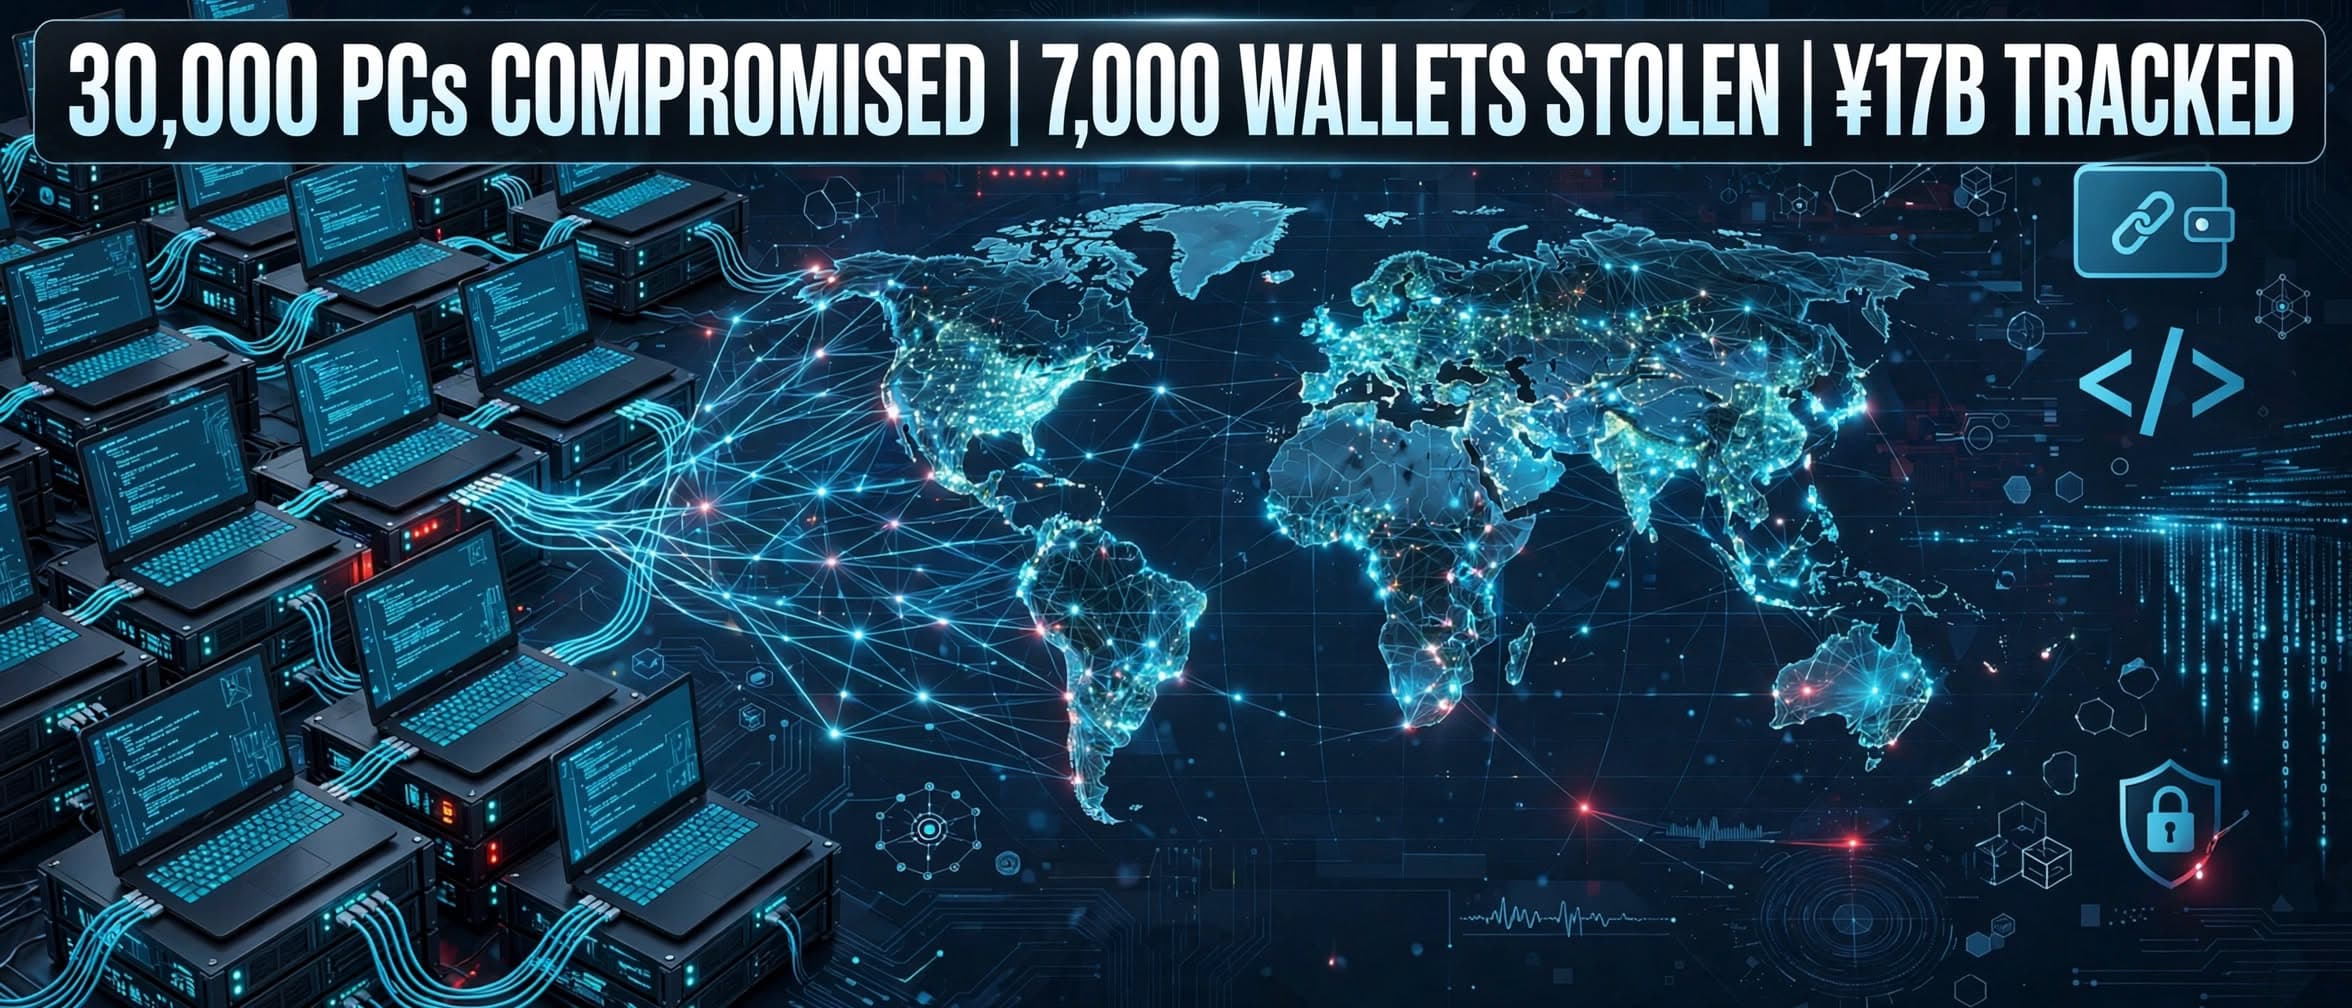
A laptop farm is not a hacking exploit. It is physical infrastructure designed to hide where the keyboard actually is.
Tokyo, Japan: The concept was detailed in the Sept. 18 joint advisory from Japan's NPA, NCO, FBI, DC3, Australia's ASD/ACSC and Germany's BND/BfV on the North Korean group WaterPlum / Contagious Interview. For the first time, Japanese police said they located and dismantled one inside Japan.
“These malicious cyber activities are a threat not only to Japan but to global security and economic activity,” Japan's PM Takaichi wrote on X, urging firms to match login IP addresses with claimed residences, check for VPN use, verify phone numbers, and treat insistence on remote work or crypto payment as a warning sign.
1. Three Layered Architecture

a) The Domestic Enabler: A person residing in the target country - Japan, the US, Europe in this case. The enabler provides what a North Korean operative cannot legally obtain: a residential address, a local ID image, a local bank account for salary, and a physical place to put hardware.
b) Clean Laptop: A standard corporate laptop issued by the victim company, or a PC purchased locally. It sits at the enabler's house, connected to a residential ISP. To any employer, the device looks like a normal employee working from home in Japan. It passes MDM checks, corporate VPN checks, and residential IP reputation checks.
c) Remote Layer: The actual operator is in North Korea, China, Russia, or elsewhere. They connect into the laptop via remote access software and through a chain of Virtual Private Servers. The advisory notes the use of commercial VPN services like NETNUT Proxy, Astrill VPN and High Speed Rabbit Proxy to further blur the origin IP.
A job application shows a Japanese address and Japanese IP. A time-tracking screenshot shows a Japanese desktop. But every keystroke is relayed from abroad.
2. Why It Makes Hacking More Sophisticated
WaterPlum is known for two parallel activities, and the farm connects them.
1. Sanctions Evasion and Legitimate Access: By getting hired as a freelance web, blockchain or AI developer through crowdsourcing platforms, the operator earns foreign currency and, more importantly, gets legitimate access to source code, cloud credentials, and internal chat platforms. Police said these earnings, amounting to hundreds of millions of yen in crypto, were sent abroad.
2. Persistence and Plausible Deniability: If a company investigates a suspicious login from Pyongyang, it finds nothing. The login is from Yokohama. The KYC passed because the ID image belonged to the enabler. If the worker is fired, they can threaten to leak source code or deface the site - cases police confirmed in the advisory.
3. Launchpad for Malware: Once inside a development environment, the same operator can introduce malicious NPM packages containing BeaverTail, InvisibleFerret, OtterCookie, OtterCandy and StoatWaffle. In the campaign from Dec 2025 to July 2026, that led to 30,000+ infected PCs and 7,000+ stolen crypto wallets across 100+ countries. Police said at least 17 billion yen worth of crypto was moved to wallets controlled by the group.
IP correlation proved the link: the same IPs that controlled the malware C2 also connected to the laptop farms and were used to apply for jobs at crypto exchange bitFlyer.
3. How to Detect It
The advisory highlights non-technical signals that were more effective than antivirus:
- Interview anomalies: Use of face-swap apps like Magicam for 2-3 minutes then camera off for "network issues," reading answers off a second monitor, background voices, low English proficiency vs. a high-level resume, insistence on remote-only work and crypto salary, refusal to relocate.
- Identity and network mismatch: Whois of applicant IP does not match claimed residence, VPN/proxy usage, phone numbers that never connect.
- Operational signals: Logins at odd local hours, multiple personas typing with different styles from one account, clipboard and credential access patterns inconsistent with the assigned task.
Defensive takeaways from the advisory: Never install a third-party remotely controllable PC in your home. For companies, restrict source code and credential access to least-privilege, invalidate sessions immediately when a contractor is suspected, and include explicit bans on undisclosed subcontracting and re-outsourcing in contracts.